Cloud Security &Compliance
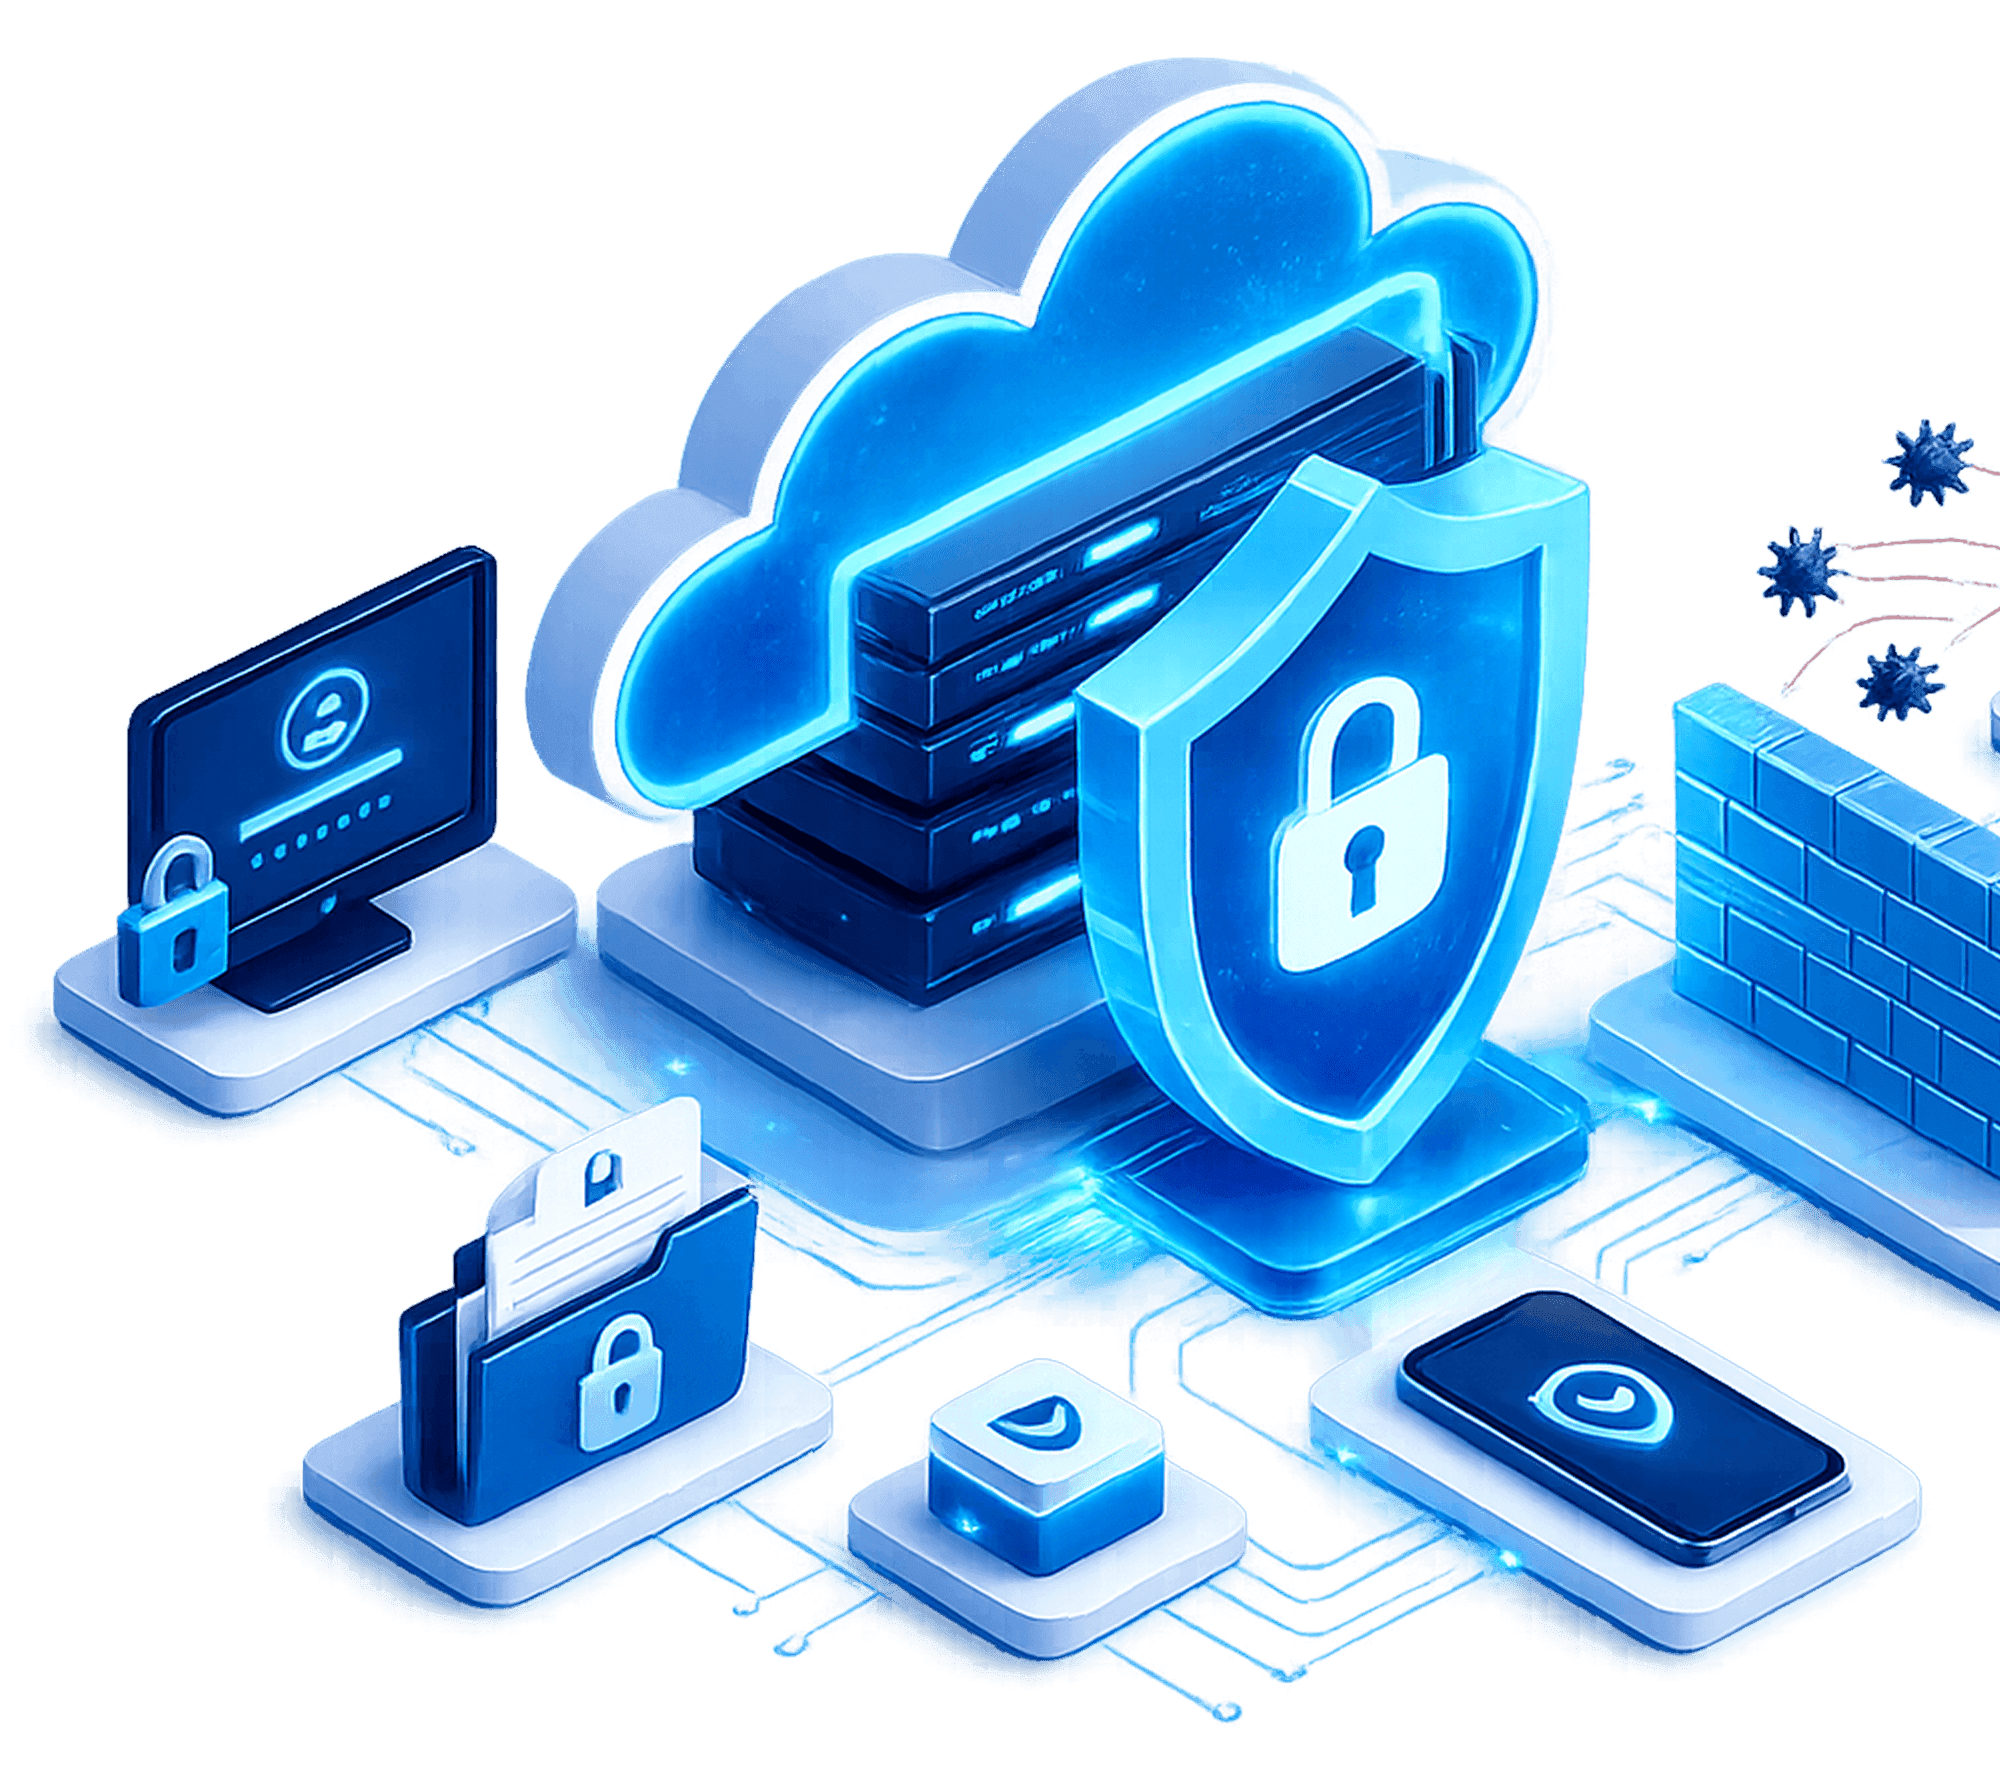
Cloud security is not a product you buy — it's a discipline you build. We design and implement defence-in-depth security architectures on AWS that satisfy the most demanding compliance requirements, including GDPR, ISO 27001, SOC 2 and CIS Benchmarks.
Core focus
From IAM hardening and network segmentation to GuardDuty and Security Hub, we ensure your posture is audit-ready from day one. Security is embedded in our delivery process — not added as a checklist item at the end.
What you get
with every engagement.
- Cloud Security Posture Assessment (CSPA)
- IAM governance framework (least privilege, RBAC, SCPs)
- Network security design (Security Groups, NACLs, WAF, Shield)
- Encryption strategy (at-rest and in-transit)
- AWS Security Hub & GuardDuty configuration and tuning
- GDPR / ISO 27001 / CIS compliance mapping report
How we run this
Engagement.
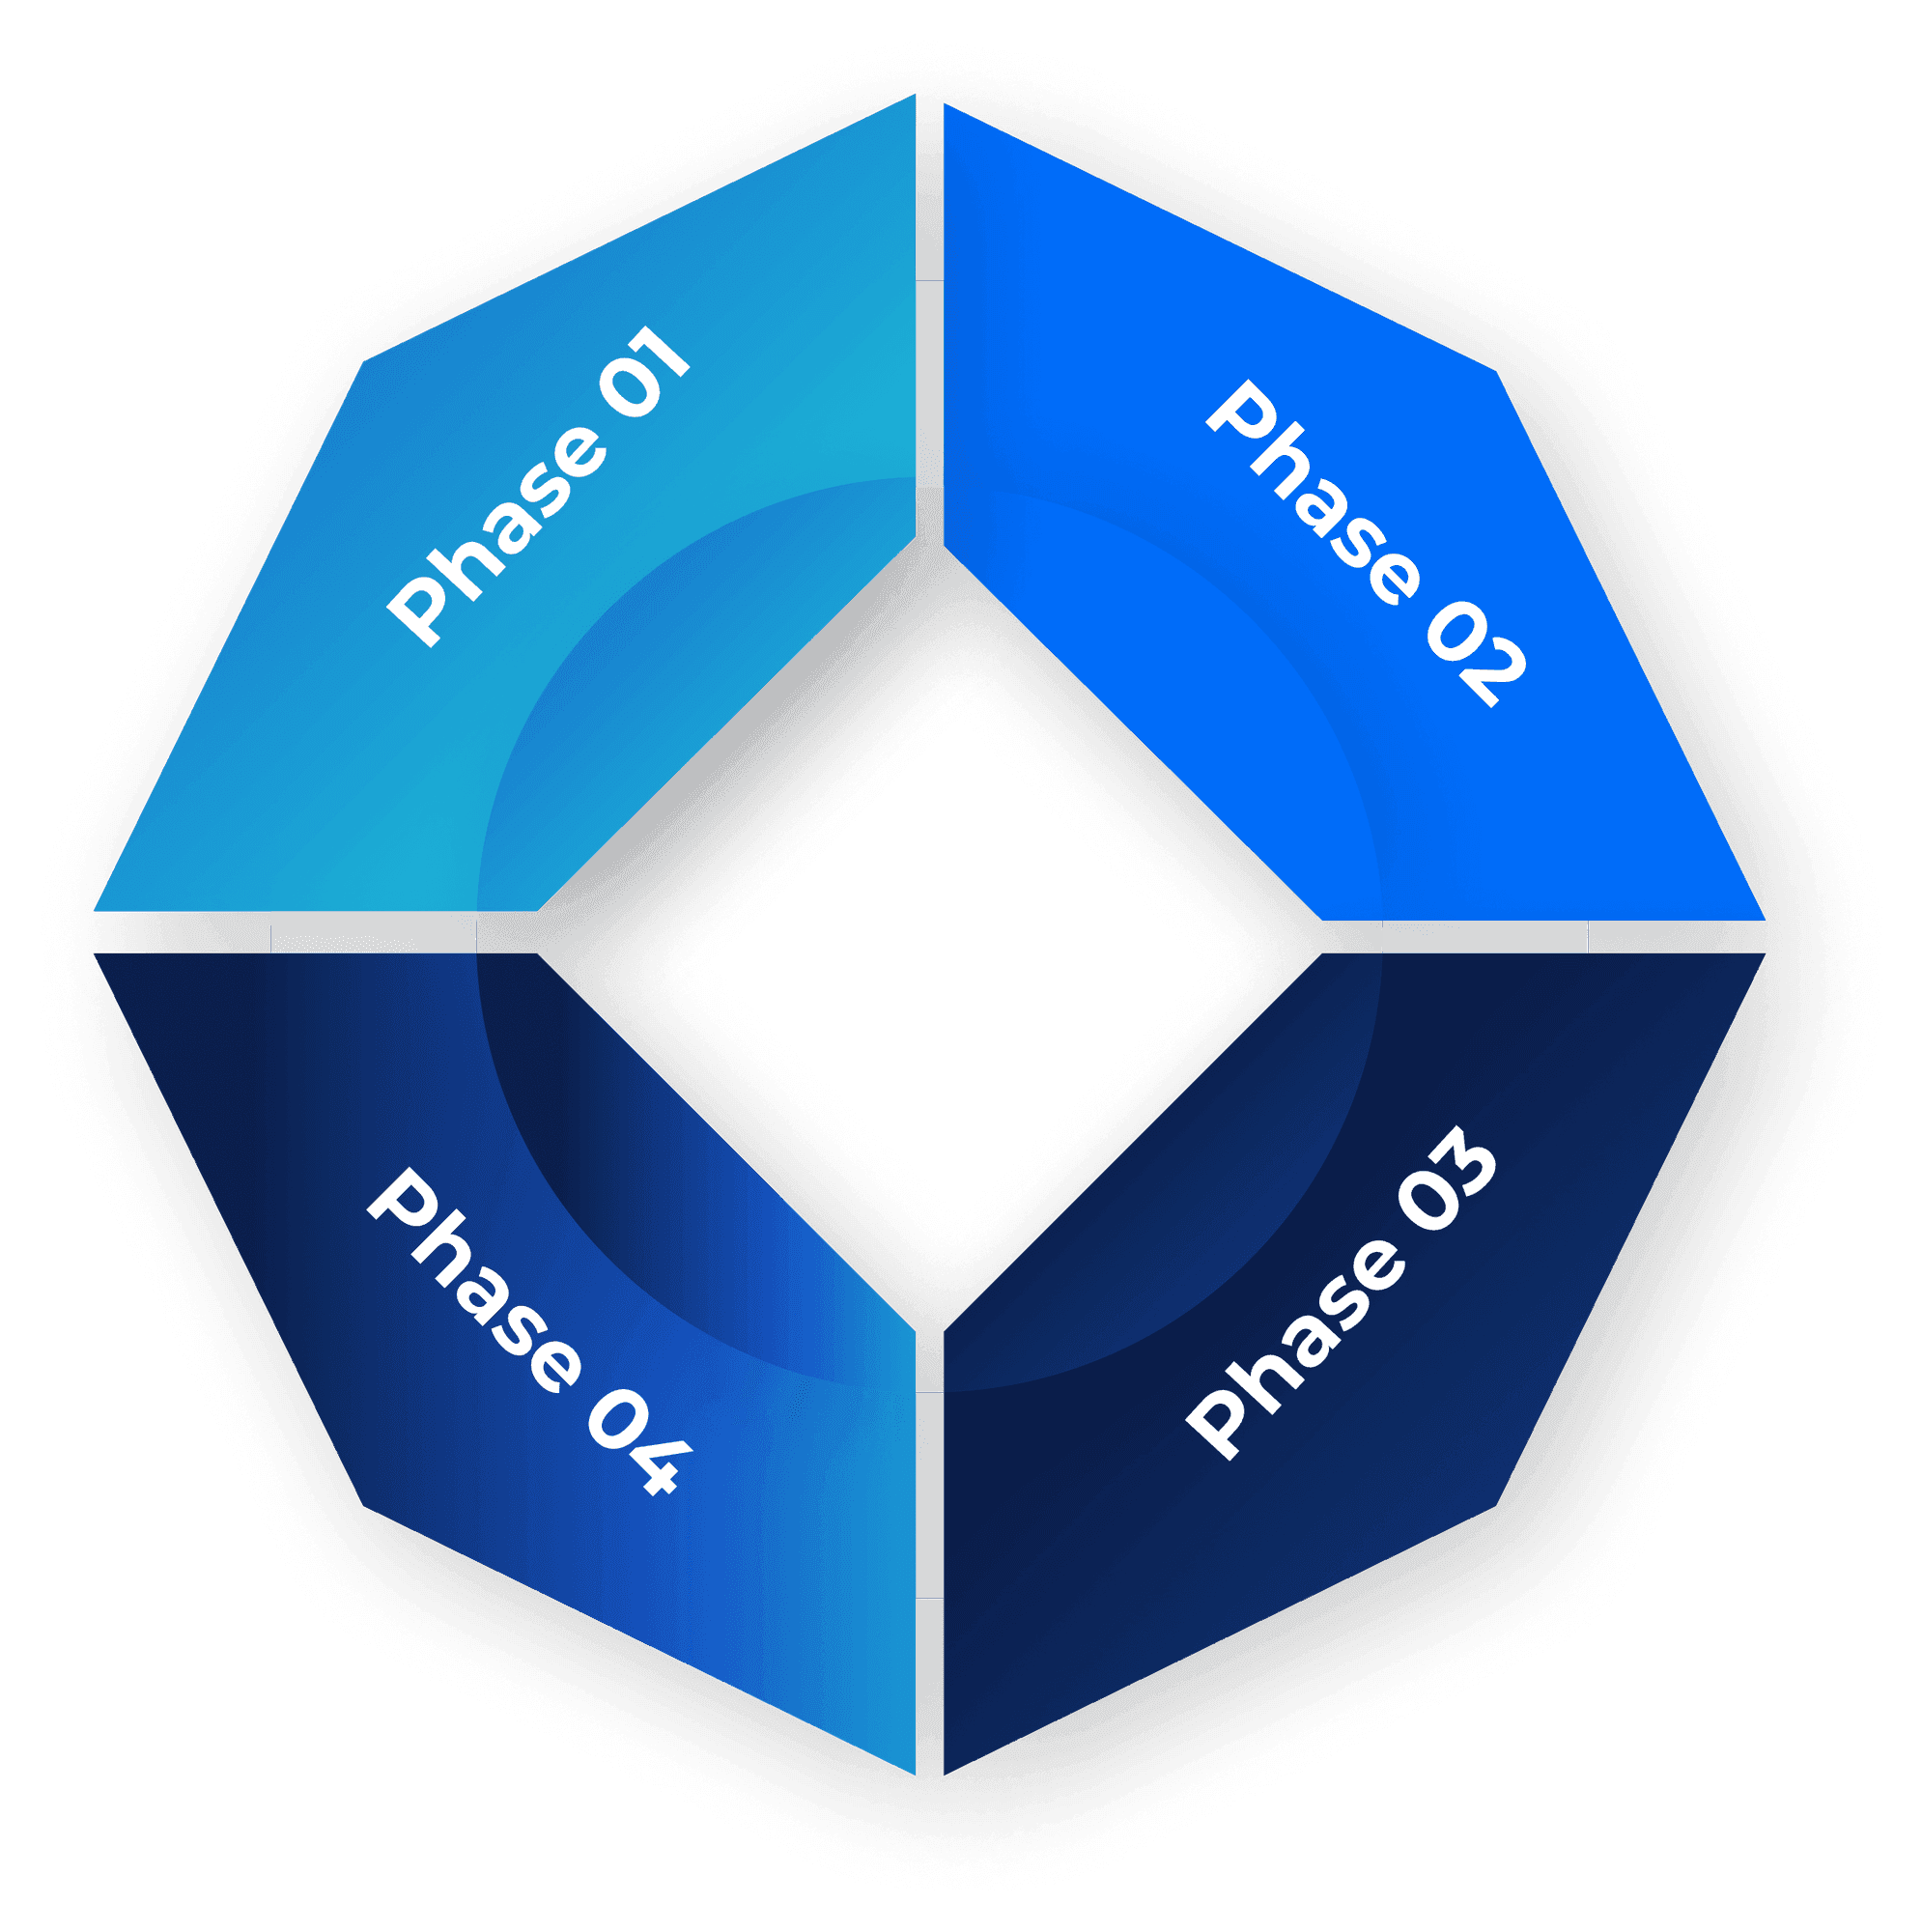
1. Security Assessment
We run a Cloud Security Posture Assessment across your accounts — identifying critical findings, misconfigurations and compliance gaps.
2. Remediation Plan
We prioritise findings by risk severity and business impact and produce a remediation roadmap with estimated effort.
3. Implement Controls
We implement the security controls, configure detective services and harden IAM — working alongside your team.
4. Validate & Report
We re-assess to confirm remediation effectiveness and produce the compliance evidence pack for your auditors.
What success looks like
after working with us.
Posture
Audit-ready from day one
Attack surface
Reduced across all workloads
Compliance
Clear evidence for regulators
Pipeline
Security controls in CI/CD
Let's discuss your
DevOps & platform engineering needs.
Fixed-price projects or ongoing managed service retainers — no lock-in, no hidden fees. Talk to a cloud architect today.